Intelligent, autonomoussecurity team built for the AI era.
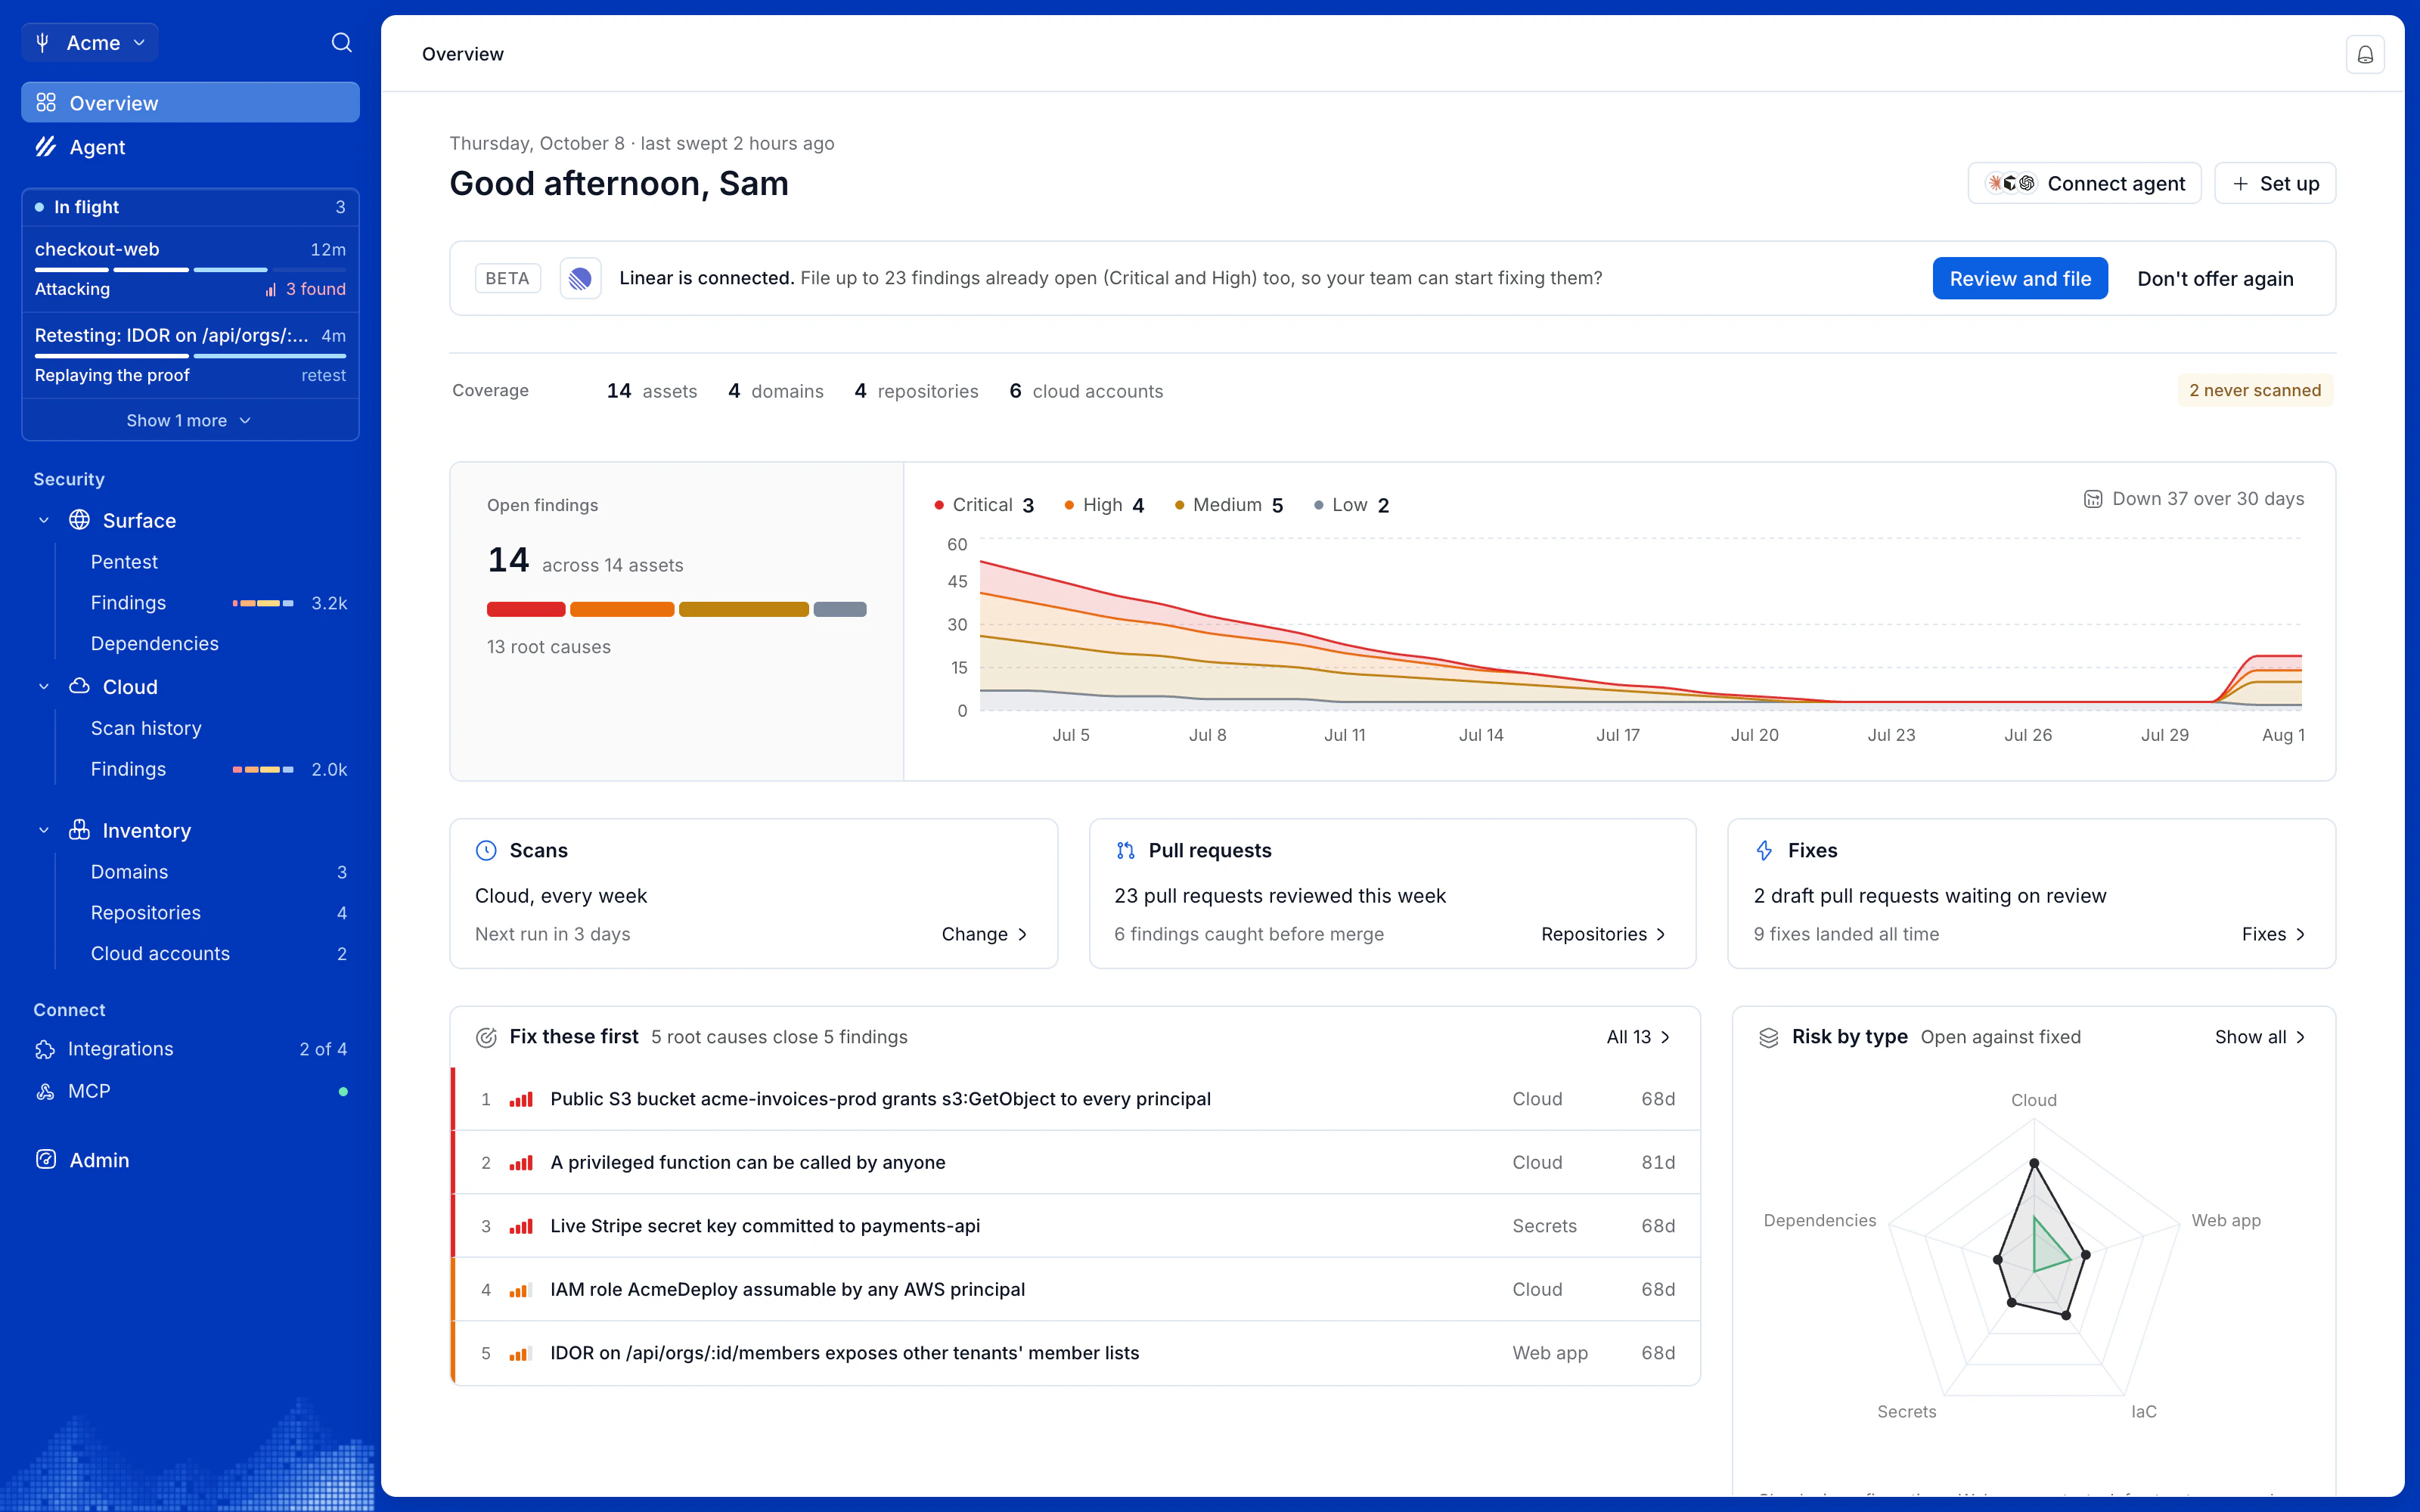
AI agents pentest your apps, review every pull request and map your cloud. Every finding comes with its proof.
Trusted by teams shipping fast

 TraceRoot
 Userlens
00HOW STRYF SEES YOUR APP
Your app, taken apartthe way an attacker reads it.
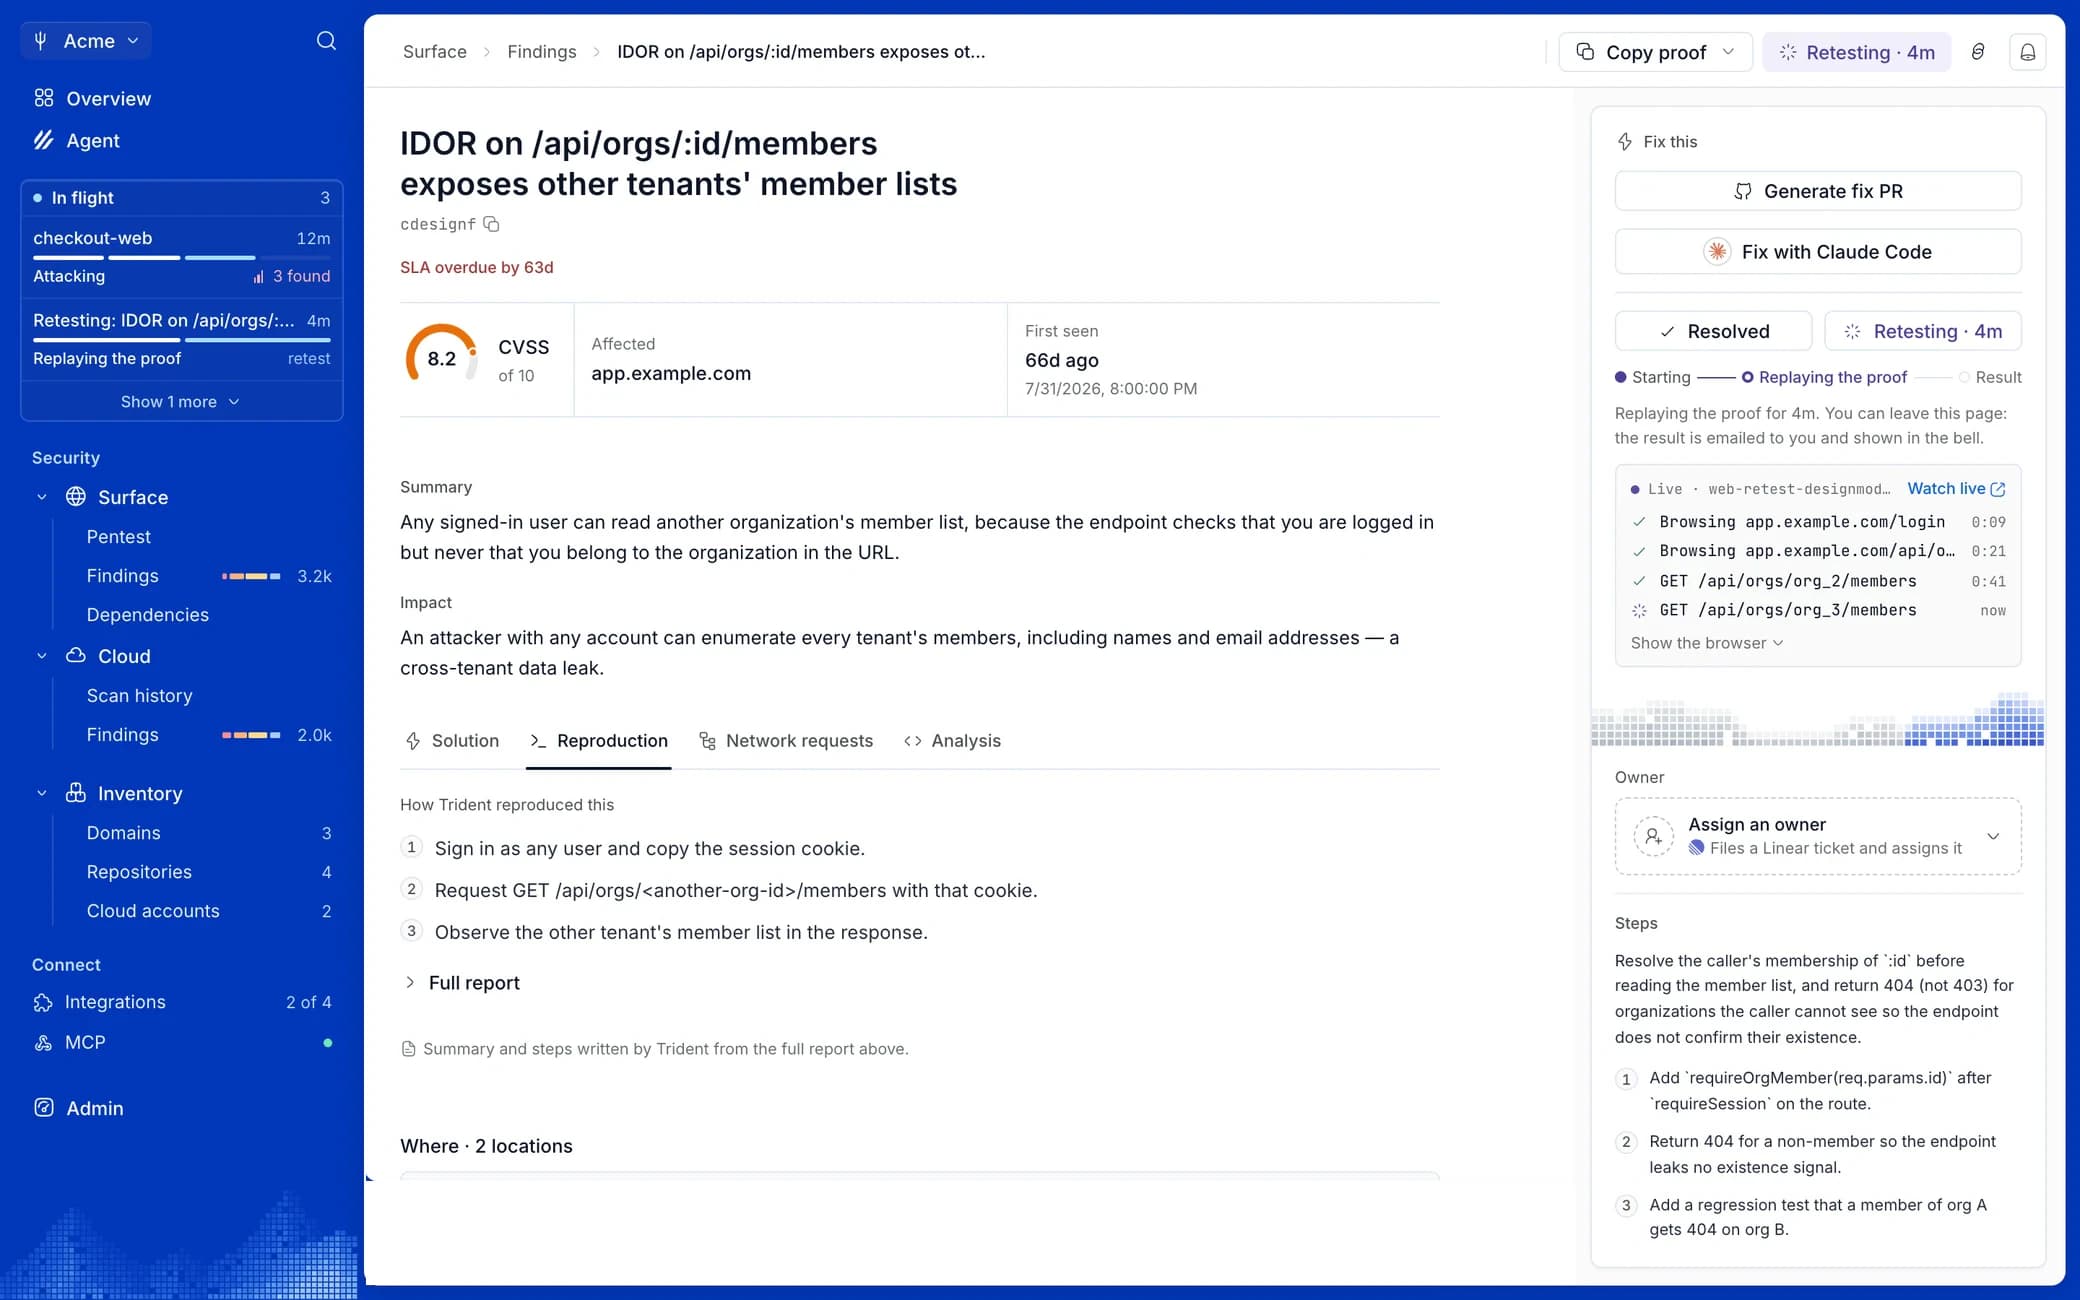
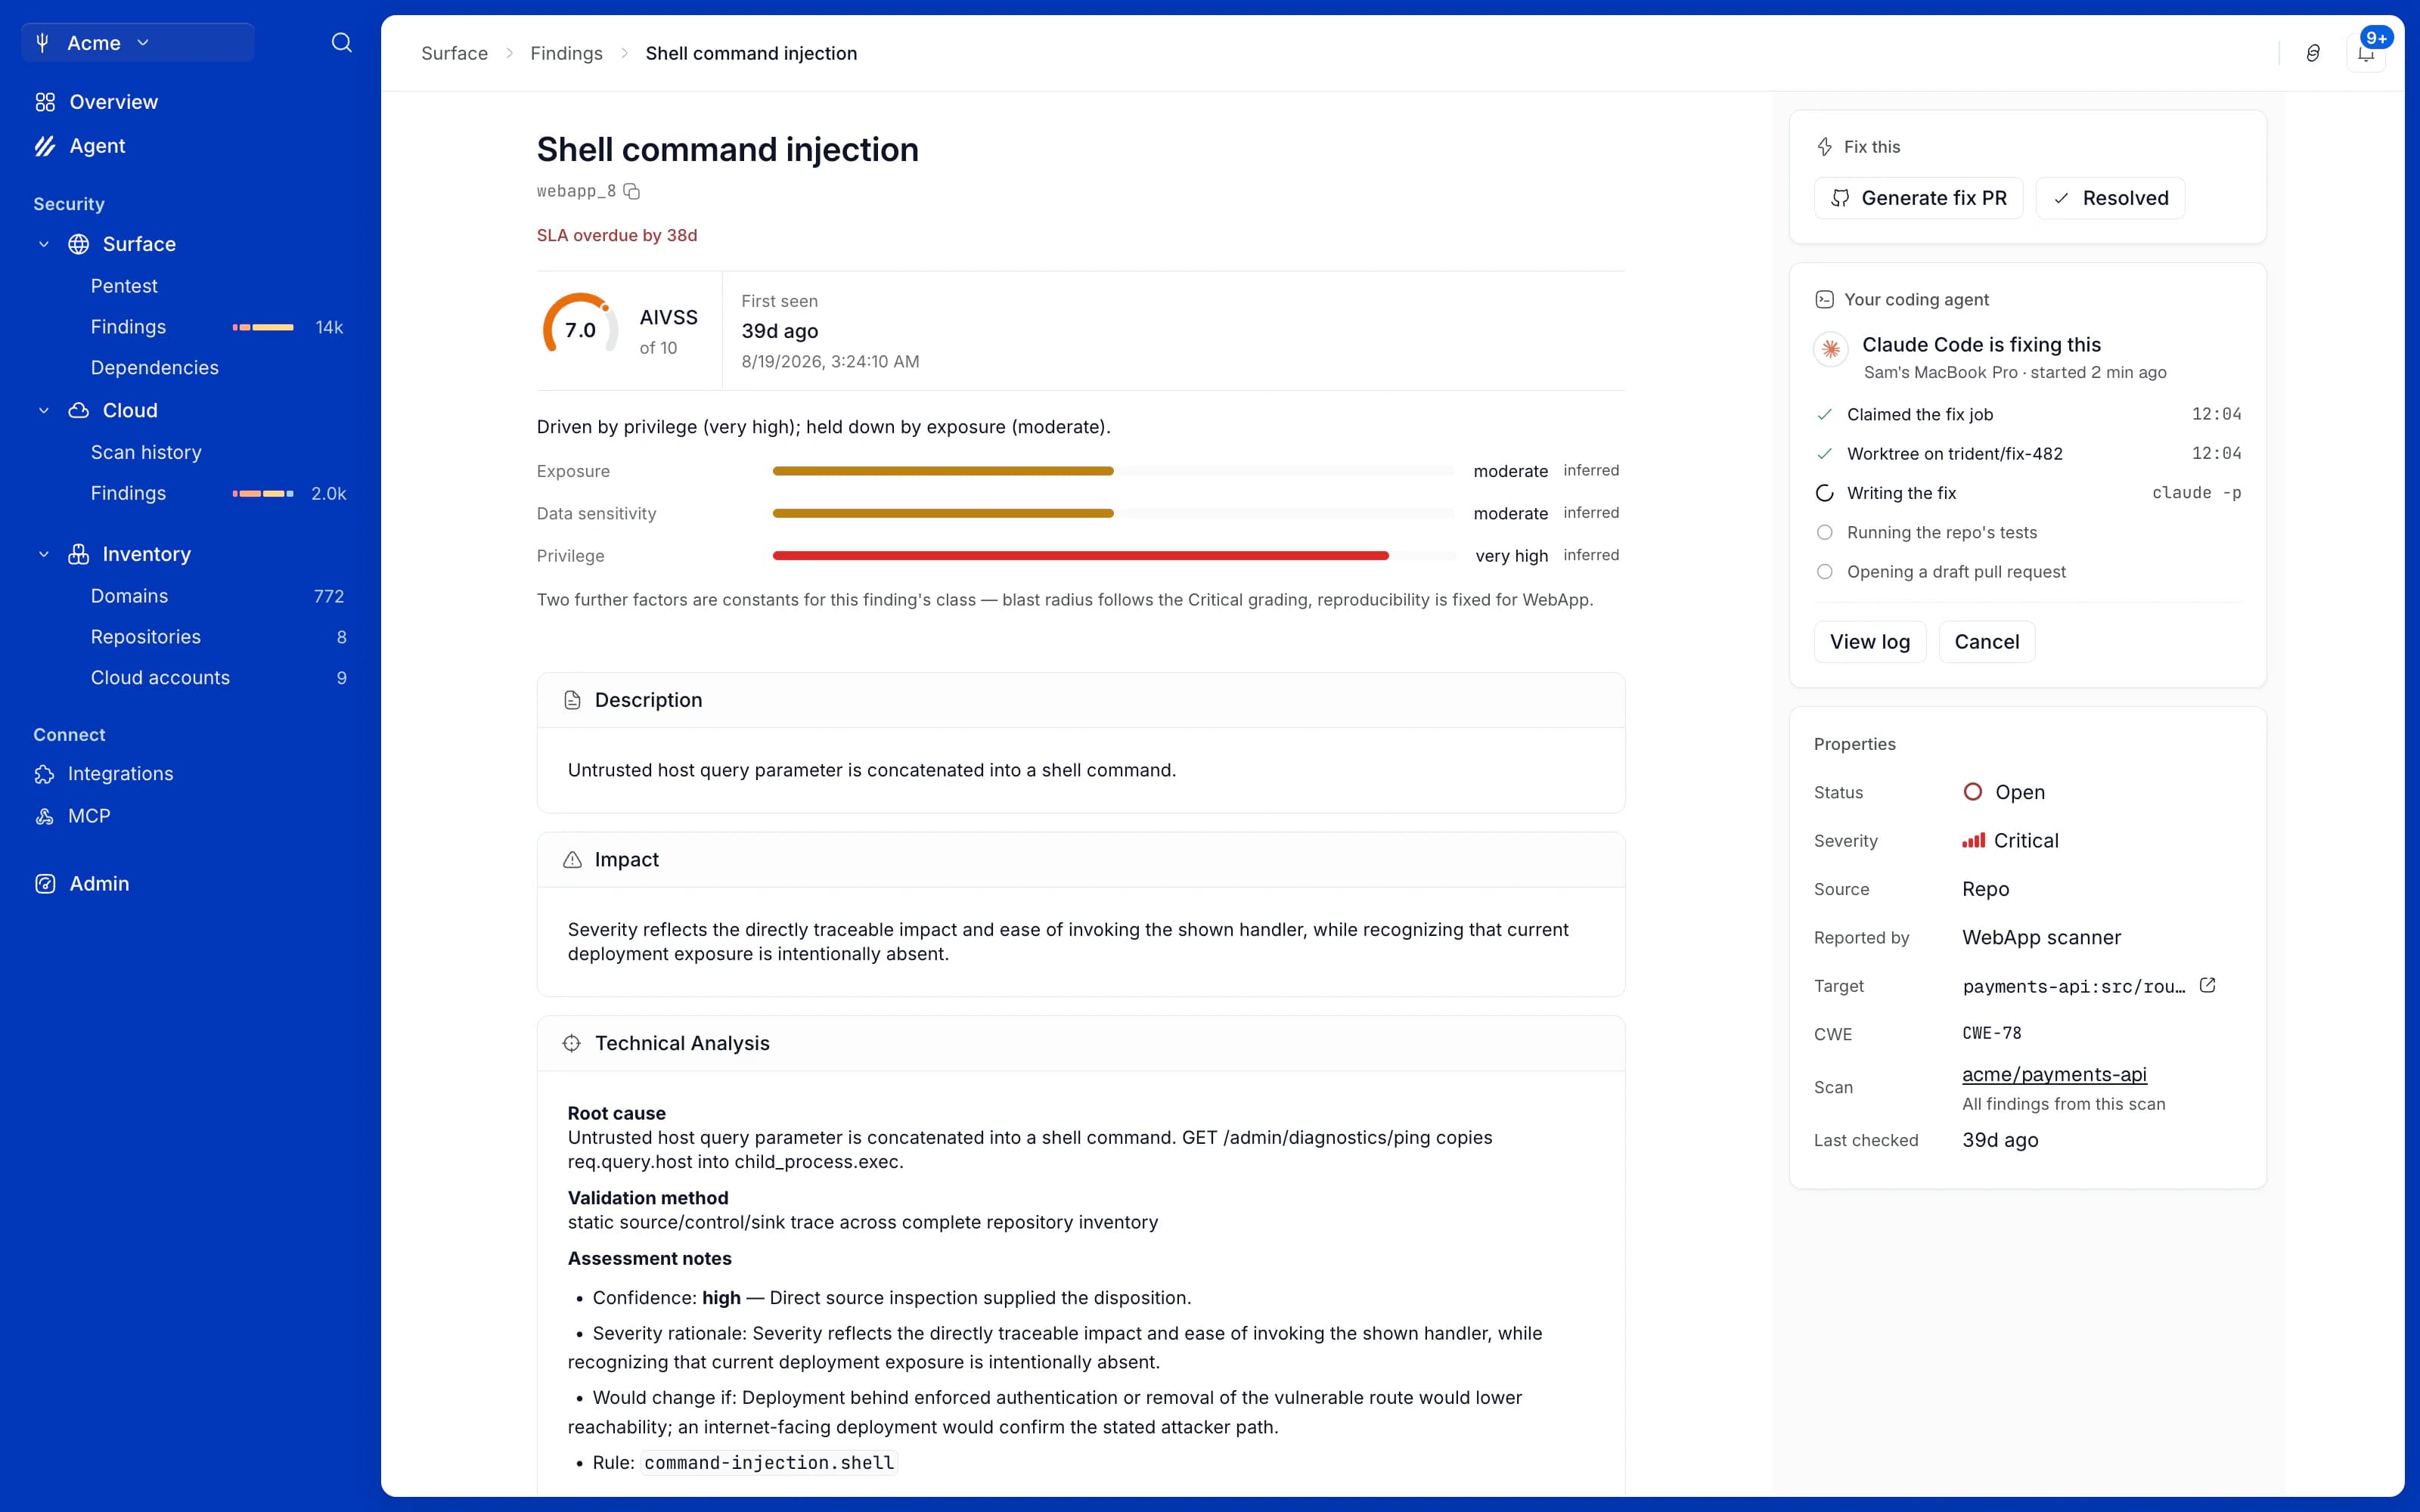
Stryf maps every route, input and auth check, joins them into candidate attack paths, then replays each one from a clean session. Only what reproduces becomes a finding.
01Watch it work
Map. Attack. Prove. Fix.
The same four steps on every scan, in the real product.
[02] WHERE IT RUNS +
Runs at every step of shipping.
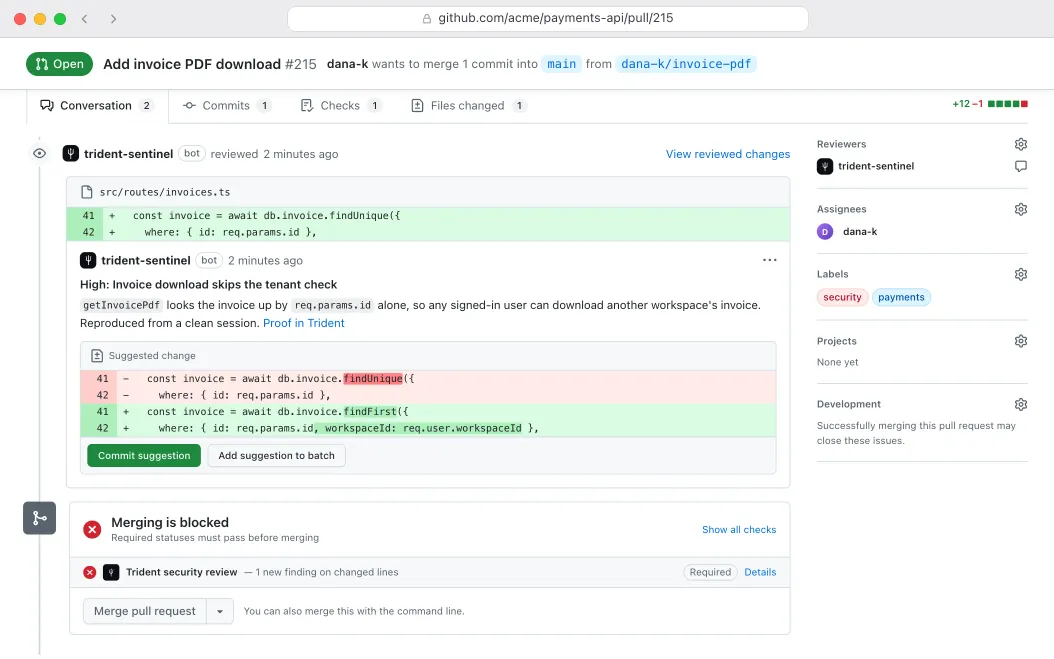
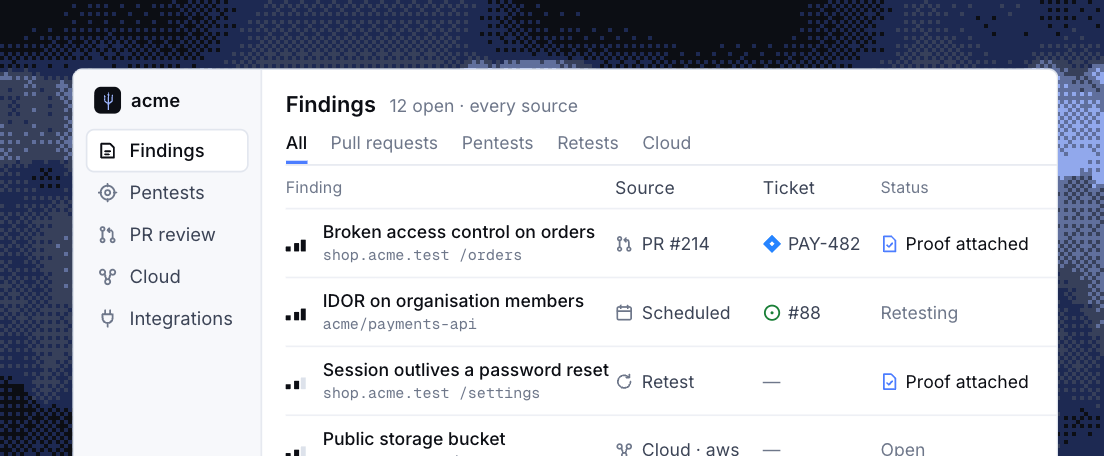
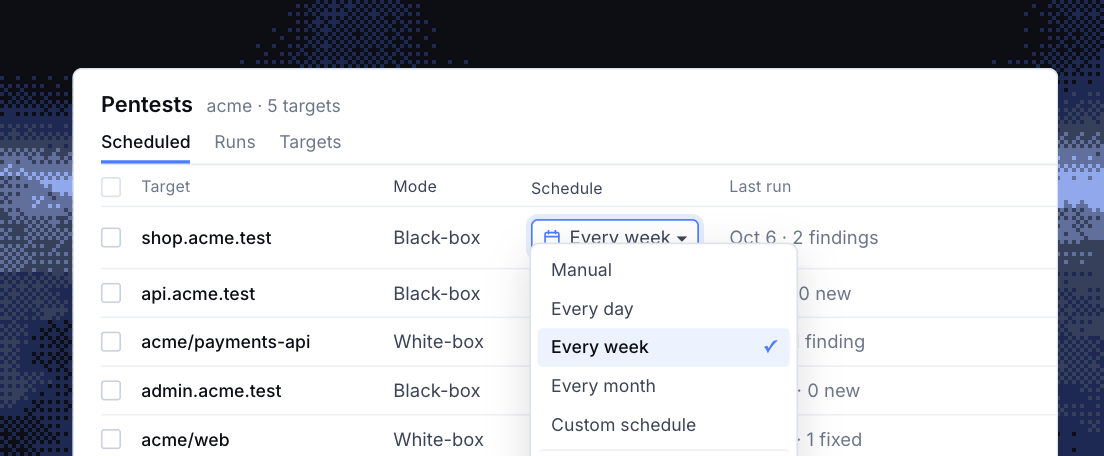
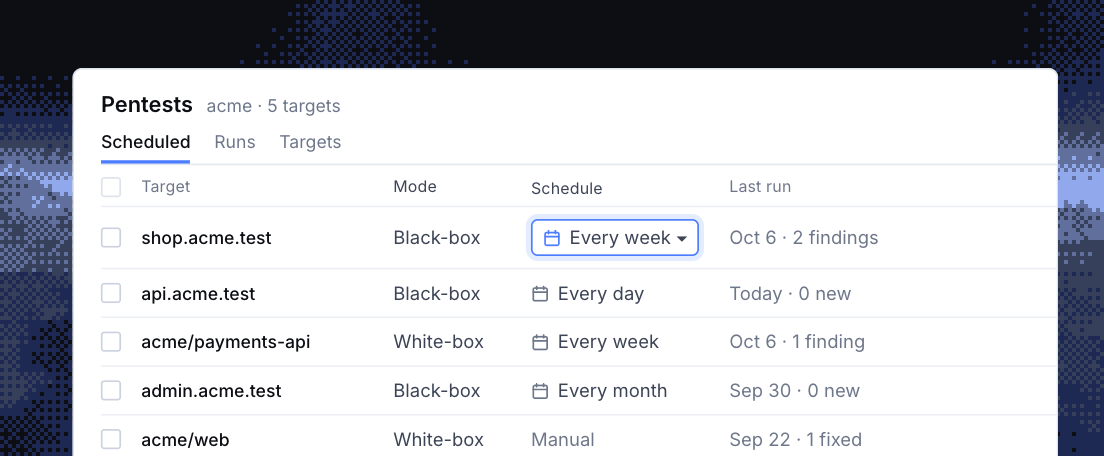
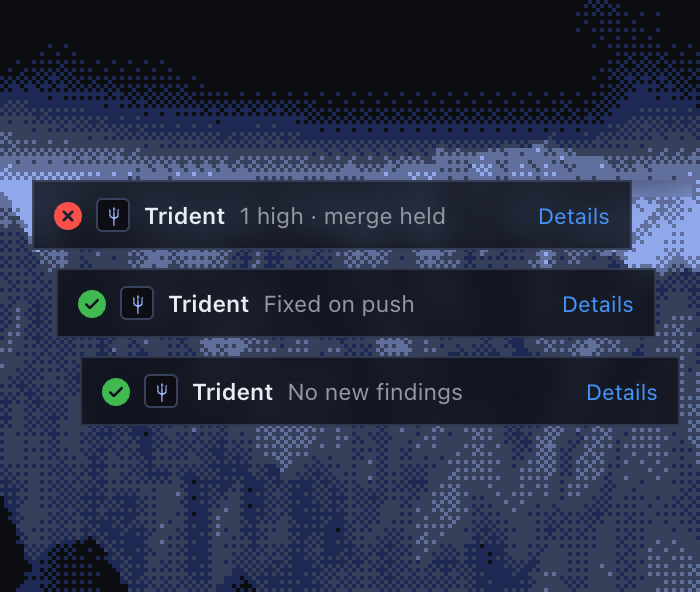
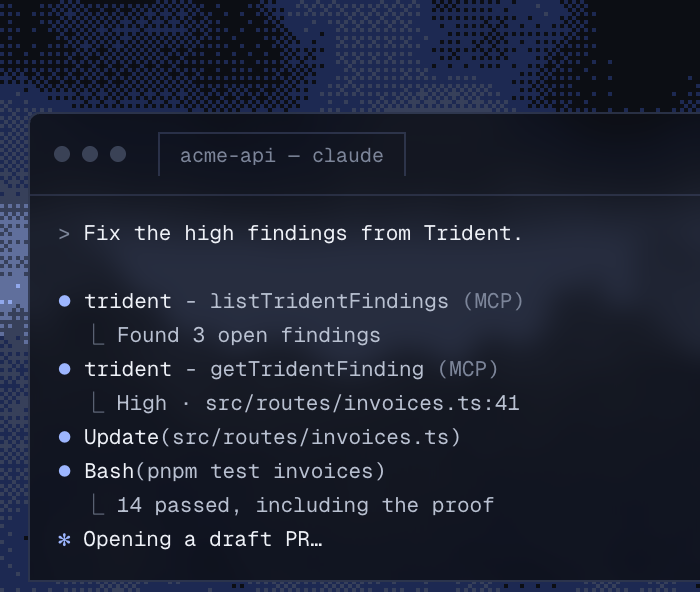
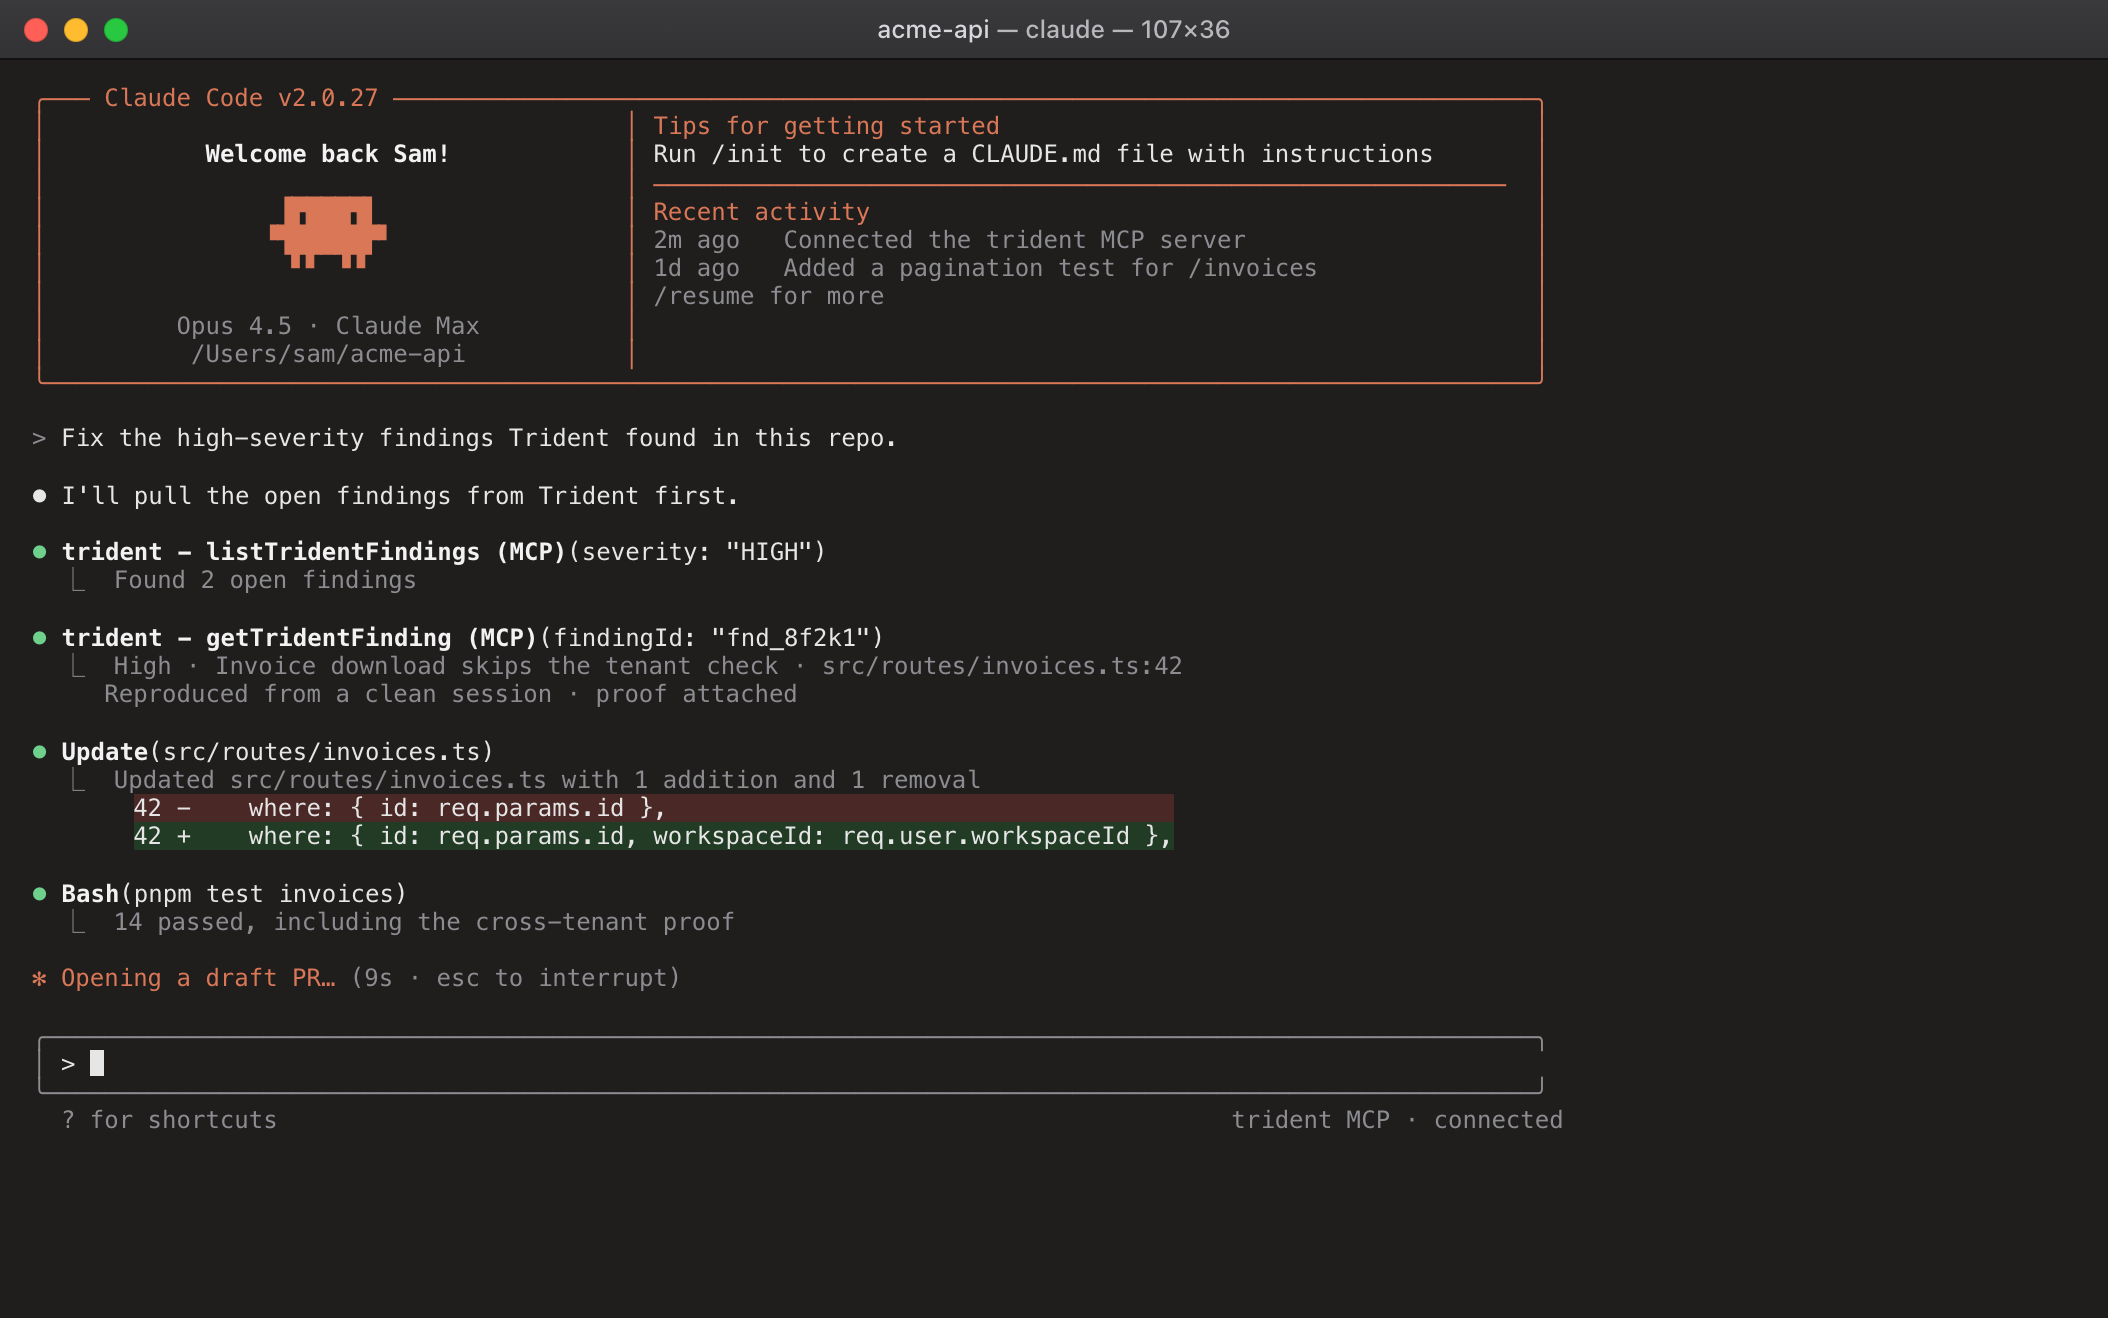
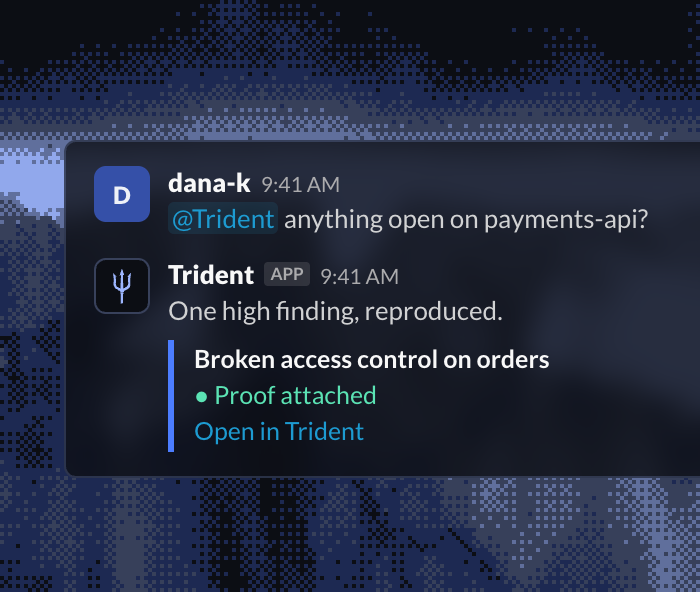
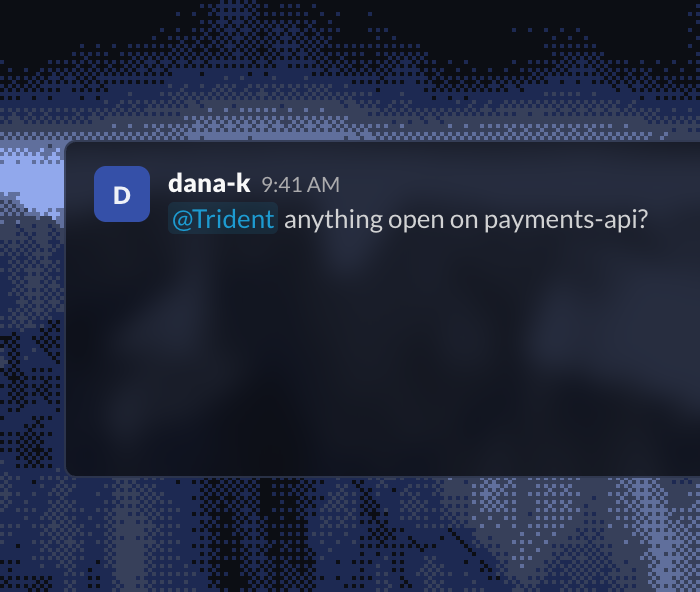
The same agents review every pull request, pentest on the schedule you set, answer in Slack and hand fixes to your coding agent. Every finding lands in one list, with its proof.
[04]TRUST+
Security that holdsitself to the same bar.
Continuous security validation with read-only cloud access.
01
Read-only access
Cloud accounts connect read-only, in minutes. Stryf maps what it can reach before the first probe goes out.05Book a demo
Show us your cloud and apps.We’ll show you the risky paths.
Tell us what you run, and the team that builds Stryf will reach out to find a time.
Common focus areas
- Cloud exposure
- Web & API pentest
- Identity paths
- Sensitive data